Sign content credentials that travel with every photo, video and document
Start Free

The C2PA Free Tier (since May 2026) includes one Level 1 Claim Signing Certificate valid for 1 year, plus 2,500 trusted timestamps per year, issued via the SSL portal.

What is a C2PA Certificate?

The cryptographic anchor for content provenance.

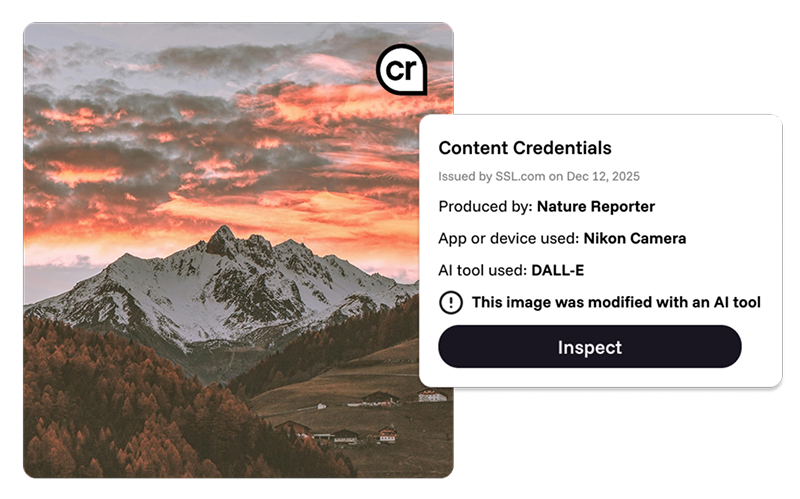
A C2PA (Coalition for Content Provenance and Authenticity) Certificate is a digital certificate used to sign a C2PA manifest, the structured provenance record embedded in a media file. The certificate proves that the manifest was created by the named entity and hasn't been tampered with since signing.

When a platform, viewer, or tool inspects a content credential, it validates the C2PA certificate signature, confirming the credential is authentic and unaltered.
SSL's C2PA Products

A C2PA Certificate lets you attach a cryptographically signed provenance record, a "content credential," to any media file. Anyone who receives the file can verify its origin, check whether it's been altered, and see an auditable chain of custody from creation to distribution. Built on the open C2PA standard, backed by Adobe, Google, Microsoft, BBC, Reuters, Sony, Nikon and the broader Content Authenticity Initiative.

Platform Certificates

C2PA Compliant claim signing certificates for online platforms. Allows Generator Products to sign C2PA claims. One certificate is need per Generator Product.

Device Certificates

C2PA Compliant Certificates delivered through our high availability API. Allows devices such as cameras, cam recorders, mobile phones, microphones or apps to sign C2PA claims.

SSL Provenance API

A fully managed SaaS (API) to add & sign C2PA + CAWG manifests to digital assets. Simplify your implementation by creating, editing & signing C2PA + CAWG manifests for your assets via a simple API calls. Explore the Provenance API

Learn more

CAWG Certificates

SSL CAWG-compliant certificates compatible with the IPTC Verified News Publisher Trust List. Add an additional attribution signature as an individual & or organization (e.g., journalist, media company).

Learn more

C2PA Plans

Trusted by

vBrick
Suspilne Ukrane
MarkAny
ArchiveOrigin
TMKR AI
Limbo
Imatag
Cloudinary
stability.ai
Numbers
Mirror

Process

Here are the steps you’ll need to go through to get stated with C2PA in your products:

1

C2PA Conformance

As a C2PA Trusted CA, SSL is required to only issue certificates for tools and devices that have passed C2PA Conformance. Find more details about the conformance process here. If you choose our premium tier we’ll be happy to support you with templates and guidance.

2

Certificate issuance

SSL issues your C2PA Certificate via our portal or API after validating your organization's identity and receiving you CSR (Certificate Signing Request).

3

Integrate into your workflow

Use the certificate in your generator product to sign content manifests.

4

Add a trusted timestamp

Request an RFC 3161 timestamp from SSL's Trusted TSA and add it to the manifest so that your content stays valid even after the certificate expires.

Compliance & standards

C2PA Specification (v2.x)

SSL issues certificates per the C2PA specification. C2PA Claim Signing certificates from Trust List CAs are the norm since C2PA 2.2.

C2PA Trust List

As of 1 January 2026, the C2PA Trust List replaced the Interim Trust List. Validators are no longer required to validate content signed via the Interim Trust List.

RFC 3161 (Time Stamping)

Trusted timestamps from SSL's TSA provide long-term validation for signed manifests

EU AI Act

Requires disclosure of AI-generated content. C2PA manifests provide a standardized, machine-readable disclosure mechanism.

Content Authenticity Initiative (CAI)

SSL is a CAI member and an active contributor to C2PA.

Frequently asked questions

Yes. Since June 2026 the SSL C2PA Free Tier includes one Level 1 Claim Signing Certificate (valid for 1 year) and 2,500 trusted timestamps per year, issued via the SSL portal. You need to apply with a valid C2PA conformance record ID. If you need Level 2 certificates, device certificates, or conformance support contact us for our Enterprise tier.

A C2PA Certificate signs the content manifest, proving it is coming from a conformant generator (e.g., a tool or device). A CAWG Identity Assertion embeds your verified organizational or personal identity inside the manifest. They complement each other: use both for maximum attribution and trust.

Without a trusted timestamp, a manifest stops being valid once the signing certificate expires or is revoked. A timestamp coming from a Trusted Time Stamping Authority like SSL lets validators confirm the claim was signed while the credential was valid, so the manifest can be validated indefinitely. See the Time Stamping Authority product page.

Yes, you can sign existing content with a C2PA manifest. However, provenance established at the point of creation is more authoritative than retroactive signing. Best practice is to sign at capture or creation.

C2PA supports JPEG, PNG, TIFF, WebP, MP4, MOV, MP3, WAV, HEIC, PDF, live video, text and others. Support is expanding as the standard matures.

Recipients can verify content at verify.contentauthenticity.org without any special software. C2PA-aware tools (Adobe apps, LinkedIn, browsers via extensions) display credentials inline.

Related products

CAWG Certificates

Add verified identity attribution inside your C2PA manifest

Time Stamping Authority (TSA)

Trusted RFC 3161 timestamps for long-term manifest validation

VMC (Verified Mark Certificate)

Authenticate your brand in email alongside content distribution

SSL.com

We’d love your feedback

Take our survey and let us know your thoughts on your recent purchase.

Privacy Overview
SSL.com

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognizing you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

For more information read our Cookie and privacy statement.

3rd Party Cookies

This website uses Google Analytics & Statcounter to collect anonymous information such as the number of visitors to the site, and the most popular pages.

Keeping these cookies enabled helps us to improve our website.

Show details